Discover Pandipedia
A growing directory of useful answers selected by the Pandi community. Search the collection or browse the latest discoveries.
2292 entries available
Financing longer lives: pensions, care and retirement technology
Financing longer lives: pensions, care and retirement technology
Longer lifespans mean retirement savings may need to support more years of income and a greater chance of needing ongoing care. This overview examines how pension reforms and public care programs respond, what long-term-care insurance can cover, and where digital tools may help people make retirement decisions.
The evidence points to a mixed-financing approach: public pension and care systems provide a foundation, private insurance may fill some care-cost gaps, and projections can help people compare retirement-income choices. But product terms vary, and the available research does not identify specific consumer retirement-planning platforms or establish that fintech tools solve the underlying affordability and longevity risks.
Policy and public programs: strengthening the foundation
Pension reform can improve the resources available in retirement, while long-term-care programs organize and finance services for people who need sustained support. The examples below illustrate different approaches rather than a single model for adapting to longer lives.
| Example | What is changing | What it addresses |
|---|---|---|
| South Korea | A 2025 pension reform schedules an increase in the mandatory contribution rate from 9% to 13% and raises the future target replacement rate from 40% to 43%. OECD projections say the reform would move the National Pension Fund’s annual deficit from 2041 to 2048 and depletion from 2057 to 2065.[1][2] | Long-term pension financing. The OECD also notes continuing high old-age poverty and recommends further measures, including extending contributions to at least the normal retirement age.[3] |
| China | World Bank-supported projects in Anhui and Guizhou expanded community, home and institutional aged-care services, assessed care needs, trained workers and supported quality standards.[4] | Building service capacity alongside broader priorities to scale up long-term-care insurance and develop a person-centered, three-tier care system.[5] |
| Uzbekistan, North Macedonia and Colombia | Programs described by the World Bank include expanded social-service access and workforce training in Uzbekistan, more licensed social services in North Macedonia, and support for national and local care systems in Colombia.[6][7][8] | Service and institutional development. The cited material does not detail the financing arrangements for long-term care in these three cases.[9] |
The policy implication is that benefits depend on more than pension promises: systems also need workable financing, trained care workers, quality oversight and accessible community-based services. The World Bank describes public stewardship and regulation combined with private-sector service delivery as one general approach; WHO’s May 2026 document is a consultation draft proposing standards, not an enacted national program.[10][11]
Long-term-care insurance: several designs, no standard product
Long-term-care (LTC) insurance helps pay for care when a person meets a policy’s eligibility rules. Private coverage may be sold on its own or bundled with life insurance or an annuity, and benefits may reimburse eligible care expenses or pay a set cash amount.[12]
- Eligibility and waiting periods: Policies can require a specified level of care need and may impose a waiting period before benefits start.[13]
- Limits and covered services: Benefit periods and daily or monthly limits vary. Some policies restrict payment to specified services or eligibility conditions, while cash benefits may offer more flexibility across care types.[14]
- Funding and payment: Public funding, mandatory health insurance, private insurance and personal contributions can coexist. Depending on the arrangement, an insurer may pay providers, reimburse fees or provide a fixed amount.[15][16][17]
- The consumer trade-off: Private cover may add support beyond public provision, but its value depends on eligibility, covered services, waiting periods and benefit limits. The available evidence does not establish a general premium comparison or a universally best-value design.[18][19]
Insurance is only one way to manage the risk of care costs. A related retirement-income trade-off is whether to convert more assets into an annuity that provides income for life or retain accessible savings that could help meet unpredictable care expenses, especially where LTC insurance is unavailable.[20]
Retirement technology: useful projections, important limits
Pension calculators and regular benefit statements can show how contributions, saving duration and investment risk may affect estimated retirement income. Many projections use a single scenario, so they should be read as estimates rather than guarantees.[21][22]
Some tools go further. Chile’s supervisor-created simulator uses stochastic investment-return modelling, including possible crises, to estimate a distribution of pension outcomes using inputs such as mortality tables and annuity rates. The research also describes Chile’s electronic annuity market as a way to reduce information gaps and support competition, but does not evaluate it as a personal planning tool.[23][24][25]
The choice of payout matters: a life annuity provides income for life, while phased withdrawals offer flexibility but do not guarantee income until death. One proposed combination is to use withdrawals earlier in retirement and a deferred annuity for later life.[26][27] However, projections depend on uncertain assumptions such as investment returns, longevity and annuity rates, and can be sensitive to the sequence of returns; complex models may also be costly to design and maintain.[28][29][30]
The research available for this report does not substantiate specific consumer-facing retirement-planning apps or online annuity-comparison platforms. It therefore supports a cautious conclusion: digital projections can help explain choices, but the evidence here does not show that they replace professional advice, guarantee outcomes or provide a complete solution to long-term care financing.
Key takeaways
- Pension reforms can improve projected system finances, but may not by themselves resolve low retirement incomes or poverty, as the South Korea example illustrates.[31][32]
- Public long-term-care programs build services and oversight; insurance can add financial protection, but policy conditions and benefit limits determine how much support a household actually receives.[33][34]
- Retirement technology is most useful when it makes assumptions and uncertainty visible. Income projections and annuity choices need to be considered alongside liquidity for unpredictable care costs.[35][36][37]
Overall, financing longevity is not a choice between government, insurance or fintech. The evidence instead describes complementary roles: public systems organize pensions and care, insurance may transfer part of the care-cost risk, and projections can help people understand retirement-income trade-offs. The main gaps are uneven care-system development, variation in insurance terms, and limited evidence here on specific retirement fintech products.
Let's look at alternatives:
- Modify the query.
- Start a new thread.
- Remove sources (if manually added).
How long is each interval in the 20 20 20 eye break rule?
Let's look at alternatives:
- Modify the query.
- Start a new thread.
- Remove sources (if manually added).
The Quantum Phone Hack: Not Today, but Prepare
Transcript
Picture your phone making a secure connection, checking an app’s identity, or installing a signed update. These protections can rely on public-key cryptography, a system that uses paired keys to protect messages and prove who sent them. The useful takeaway is this: a powerful future quantum computer could threaten some of those protections, but it would not automatically unlock every smartphone. A sufficiently capable, fault-tolerant quantum computer could use an algorithm called Shor’s algorithm to break the mathematics behind some widely used public-key systems. That could expose private keys, enable forged digital signatures, or help decrypt communications recorded today. No quantum computer exists at the required scale, and when one might arrive is uncertain. So this is not a story about phones being cracked by quantum computers today. It is a warning about what could happen if vulnerable systems are not replaced in time. Most symmetric encryption, another way to protect data, is considered more resilient; larger keys can help compensate for quantum search. But data captured now could matter if it must remain private for years. There is a response underway. In 2024, the National Institute of Standards and Technology finalized three post-quantum cryptography standards, designed to resist conventional and quantum attacks. The migration means providers need to find vulnerable systems and update software and services. Phone owners generally depend on device, app, browser, and service providers to make those changes. The plot twist is not that quantum computers have cracked your phone. It is that preparation has to start before they can. Keep devices and apps updated, and look for providers communicating their plans for post-quantum security.
Let's look at alternatives:
- Modify the query.
- Start a new thread.
- Remove sources (if manually added).
Differential privacy in quantum data sharing
Differential privacy in quantum data sharing
Differential privacy is a way to limit what an analysis reveals about any one person, even when its results are shared. It could help make quantum analyses of sensitive datasets safer to release, but the guarantee depends on how privacy is defined and implemented.
What differential privacy guarantees
A randomized analysis is differentially private when its output would be nearly as likely whether or not one person’s record was included in the dataset. Formally, the probabilities of any possible output differ by at most a multiplicative factor set by ε, plus an optional small additive allowance δ. Smaller ε means stronger protection; δ permits a small probability of additional leakage.[1][2][3]
The practical aim is to make it difficult to infer an individual’s participation from the released result, even if an observer has other information. This protects against a particular kind of inference from outputs; it is not, by itself, a guarantee that all parts of a data-sharing system are secure.[4][5]
Why it matters for quantum analysis
Quantum algorithms may analyze sensitive data, so their outputs can also raise questions about what can be learned about the people represented. Differential privacy can be incorporated at different points, including data preparation and quantum-state encoding, inside a circuit, or at measurement and output. Researchers have also studied whether quantum encoding, subsampling, or compositions of quantum operations can amplify privacy, under particular assumptions.[6][7][8]
One proof-of-concept hybrid approach clipped and noised gradients during the classical optimization of a variational quantum circuit. It reported accuracy alongside privacy protection in simulated classification experiments, but the quantum model was simulated on a classical computer, so it does not establish how well the method works on quantum hardware.[9]
Integration challenges
- There is no unified benchmarking approach: studies differ in how they define neighboring quantum states, measure distance, and introduce randomness.[10]
- Added noise can affect analytical usefulness, so privacy protection must be assessed alongside the utility of the result.[11]
- Researchers call for built-in differential-privacy tools in quantum simulators and cloud platforms, experimental privacy audits, and a dedicated accountant to track cumulative privacy loss across repeated mechanisms.[12][13][14]
- Theoretical privacy amplification results rely on stated assumptions; they do not show that every quantum algorithm or device automatically provides stronger protection.[15]
In short, differential privacy offers a promising way to limit what shared quantum-analysis results reveal about individuals. Practical confidence will require clear privacy definitions, accounting across repeated analyses, and validation of both privacy and usefulness on real systems.[16][17]
Let's look at alternatives:
- Modify the query.
- Start a new thread.
- Remove sources (if manually added).
When the TV became the stage
Let's look at alternatives:
- Modify the query.
- Start a new thread.
- Remove sources (if manually added).
Frogs, But Make It Wolverine
Let's look at alternatives:
- Modify the query.
- Start a new thread.
- Remove sources (if manually added).
Rebuilding institutional trust in the digital era
Rebuilding institutional trust in the digital era
Digital tools can help close the trust gap when they make government easier to scrutinise, give people a real say, and deliver services that work for everyone. They are not a shortcut to trust: the evidence more often documents improvements in participation, service delivery, or government capacity than proves that a particular platform directly increased public trust.[1][2][3]
Executive summary
- Publish information people can use to understand decisions, spending, and results, then connect it to oversight and public participation.[4][5][6]
- Make participation consequential: show how public input was considered and what happened next. In the OECD’s 2024 Trust Survey, 53% said the political system did not allow people to influence government, and 32% thought governments likely to adopt views expressed in consultations.[7][8]
- Improve digital services around user needs, with accessible design, reliable delivery, privacy and security safeguards, human help, and non-digital alternatives.[9][10][11]
- Treat international examples as practical lessons, not proof of causation: available evaluations often report activities or capacity gains rather than measured changes in trust.[12][13][14]
1. Make transparency usable and accountable
Transparency is most useful when people can follow the chain from a government decision to the money spent and the results achieved. Governments can proactively publish decision-relevant information and make budget, procurement, spending, and activity data searchable, machine-readable, timely, and reusable.[15][16][17]
Disclosure alone is not accountability. Pair publication with public participation and scrutiny by legislatures, auditors, and other oversight bodies. Information should be clear, reliable, relevant, and accompanied by metadata that explains how it was collected and any known quality limitations; privacy and security remain valid reasons for proportionate restrictions.[18][19][20][21]
A practical pitfall is mistaking volume for openness. A large data dump may leave people unable to tell what was decided, how funds were used, or whether services improved. Prioritise information citizens need, maintain it through clear responsibilities and adequate staffing, and ask users what data would be useful.[22][23][24][25]
2. Make participation meaningful and inclusive
Digital participation can strengthen trust when people can see that their contributions were considered, rather than simply collected. In the OECD’s 2024 survey, 69% of people who felt they had a say in government reported high or moderately high trust, compared with 22% of those who did not; this is an association, not evidence that a platform caused higher trust.[26][27]
Build a visible feedback loop: explain how input informed a decision, publish outcomes, and make institutions responsible for follow-up. Design platforms with users, use clear and accessible language, and offer accessible formats, human assistance, and offline routes so people are not excluded by disability, connectivity, literacy, or digital skills.[28][29][30][31]
Examples include Italy’s ParteciPA, which hosted 46 participatory processes and received more than 4,000 citizen inputs, and Croatia’s e-consultation system, which publishes comments on proposed regulations and responses to each comment. The Netherlands’ OpenStad, Barcelona’s Decidim, and Portugal’s Participa.gov are also documented as platforms for activities such as consultation, voting, participatory budgeting, and submitting ideas. These are examples of participation mechanisms, not demonstrated causal increases in trust.[32][33][34][35]
3. Improve services people can rely on
Service reliability, access, quality, and responsiveness are closely connected with trust in government. Improve services by simplifying end-to-end journeys across agencies, designing with users, and making online services accessible and intuitive. Keep human support and non-digital alternatives available for people who cannot or do not wish to use digital channels.[36][37][38][39]
Shared digital infrastructure, such as secure digital identity and responsible data-sharing systems, can reduce repeated requests for information and support joined-up services. But governments need privacy-by-design, security safeguards, transparent governance, and clear explanations of how algorithms are used; they should also monitor whole-service outcomes and improve services iteratively using user feedback and performance data.[40][41][42][43][44]
Serbia’s World Bank-supported EDGE project offers a capacity-building example: it trained more than 4,000 public servants in data protection and cybersecurity, tailored training to different roles, extended training to local service institutions, and strengthened national security infrastructure. The account presents lessons for trusted digital government, but does not report a measured public-trust impact.[45][46][47]
4. International examples and what they show
These cases illustrate different ways to put transparency, participation, or capacity-building into practice. Their results should be interpreted cautiously: documented activity or improved capacity does not by itself establish that public trust rose.
| Example | What it demonstrates | Evidence and caveat |
|---|---|---|
| Philippines: CheckMySchool | Citizens could inspect school information, report problems, and engage officials; the initiative began with textbook delivery and later included issues such as sanitation, staffing, and standards compliance.[48][49] | A transparency and accountability example; the review cautions that case studies have limited transferability and that impact evaluations of open-government-data initiatives are scarce.[50] |
| Italy: ParteciPA; Croatia: e-consultation | ParteciPA hosted participatory processes and collected citizen input; Croatia’s system publishes consultation comments and responses.[51][52] | Shows participation and visible follow-up in practice, but the cited evidence does not establish that either platform alone raised trust. |
| Open Government Partnership country-capacity support | Supported technical assistance, peer learning, and government-civil society co-creation for open-government reforms.[53] | The November 2023 progress report rated progress “Satisfactory,” but did not establish a measured increase in public trust.[54] |
| Serbia: EDGE project | Built public-sector data-protection and cybersecurity skills and strengthened security infrastructure.[55][56] | Useful capacity-building lessons, not a measured trust-impact evaluation.[57] |
5. Pitfalls to avoid and a practical sequence
- Do not equate publishing with transparency: provide understandable information about decisions, spending, responsibilities, performance, and outcomes.[58][59]
- Do not collect public comments without follow-through. Explain how input was used and provide a route for accountability; consultation that feels like a box-ticking exercise can deepen distrust.[60][61]
- Do not make essential participation or services digital-only. Gaps in skills, literacy, devices, or connectivity can exclude people; retain human help and offline access.[62][63][64]
- Do not treat launch as success. Platform and service initiatives need sustained funding, clear accountability, institutional capacity, and monitoring; service and digital-program impacts can be mixed, while infrastructure may require substantial upfront costs.[65][66][67]
- Start with user needs and a baseline, then improve in stages: prioritise high-value information and services, set clear standards and responsibilities, protect privacy and security, and track whether people can use the service and whether their feedback changes decisions.[68][69][70][71]
Conclusion
The strongest approach is to treat digital transparency, participation, and service delivery as one accountability system: publish information people can use, give them a meaningful way to influence decisions, show what happened next, and deliver accessible services with strong safeguards. Measure whether these changes improve access, responsiveness, accountability, and user experience, and do not claim a trust effect unless it is actually evaluated.[72][73][74]
Let's look at alternatives:
- Modify the query.
- Start a new thread.
- Remove sources (if manually added).
Building an AI ethics committee that can act
Building an AI ethics committee that can act
An AI ethics committee helps an organization identify and manage risks before and after AI systems are deployed; this guide gives you a practical charter, membership model, review workflow, escalation path, and sector-specific starting points. Its value depends on clear authority, accountable system owners, and a review process that scales with potential harm, rather than on the committee’s name alone.[1][2][3]
Treat the committee as one part of governance, not as a substitute for legal, security, privacy, or operational responsibility. A useful division is for the committee to set policy and oversee risk, while engineering builds and maintains systems and business owners remain responsible for the purpose and outcomes of their use cases.[4][5]
1. Write a charter that defines authority
The charter is the committee’s operating contract. It should be formally approved and reviewed periodically, and make explicit whether the committee advises, approves, or can pause or stop a deployment. State which decisions are delegated, which require committee review, who can override or pause a system, how quorum and voting work, and how decisions and dissent are recorded.[6][7][8][9][10]
- Mandate and scope: Set policy and standards, triage proposals by risk, review high-risk uses, oversee incidents and monitoring, and report AI risk to senior leaders. Define coverage for internally built systems, vendor tools, models, and use cases, with a way to expand the scope as organizational needs change.[11][12][13][14]
- Decision rights: Identify what the committee may approve, reject, defer, or recommend for executive or board decision. Specify approval thresholds, escalation routes, and who may restrict or stop AI-driven processes.[15][16]
- Accountability: Name the people responsible for proposing, assessing, approving, operating, monitoring, and escalating each system. A RACI matrix, which identifies who is responsible, accountable, consulted, and informed, can make these assignments visible.[17][18]
- Records and reporting: Require decision rationales, minutes, conflicts and recusals, incidents, remediation actions, and a system inventory. Set the reporting audience and schedule, and cover portfolio status, risk posture, incidents, audit findings, and escalations.[19][20][21]
Use this as a copyable starting outline, then have the organization’s appropriate leaders approve it. It turns the charter elements above into fill-in fields; the specific authority and thresholds must be chosen for your organization.[22][23][24]
AI GOVERNANCE / ETHICS COMMITTEE CHARTER

Purpose and mandate:
[Policies, oversight responsibilities, and intended outcomes]

Scope:
[Systems, vendors, use cases, lifecycle stages, and risk triggers covered]

Authority and decision rights:
[Advisory / approval / pause authority; delegated decisions; quorum; voting; override authority]

Membership and appointments:
[Roles, selection criteria, terms or review cycle, alternates, external advisers]

Accountability:
[Owner for proposal, assessment, approval, operation, monitoring, incident response]

Review and escalation:
[Risk tiers; required reviewers; escalation triggers; urgent review route]

Conflicts and records:
[Disclosure, recusal, minutes, decision rationale, dissent, evidence retention]

Reporting:
[Audience, schedule, portfolio and risk information, incident and remediation updates]

Approval and maintenance:
[Approving authority, effective date, review date, amendment process]
2. Select members for expertise and meaningful challenge
Build a cross-functional committee that combines decision authority with the expertise to question a proposal. Common roles include an executive sponsor or chair, a program manager or secretary, legal, privacy, security, risk and compliance, AI or engineering, data, and product or business representatives. Include a business owner for the use case, but keep oversight distinct from the team building the system.[25][26][27]
Add ethical expertise and perspectives from people affected by AI, such as customers, employees, partners, researchers, or communities; for sensitive or high-impact proposals, consider external experts or affected-community advocates. Use transparent appointment criteria, check conflicts of interest, and periodically revisit whether the committee’s skills and perspectives still fit its work.[28][29][30][31][32]
Protect the committee’s ability to raise concerns: members should have access to relevant information and a route to senior leadership or the board, while conflicts should be disclosed and handled through recusal or abstention. External members can add independence, but may have less timely access to internal information; define the trade-off rather than assuming one structure is always best.[33][34][35][36][37]
3. Use a gated, risk-based review workflow
Run reviews through a central AI inventory or registry. Require an accountable owner, pass criteria, and retained evidence at each gate, and make required review and sign-off prerequisites for production. Reassess risk at procurement, deployment, and when the system or its context changes.[38][39][40]
From proposal to monitored system
- Intake: Before development or procurement, collect the purpose, owner, intended users, data sources and sensitivity, model or provider, deployment context, and whether the system makes or informs decisions. Register the workflow and downstream uses, not just the model.[41][42]
- Tier and route: Consider severity, likelihood, reversibility, affected people, decision impact and autonomy, data sensitivity, failure consequences, and ability to intervene. Route high-impact uses, including decisions affecting rights, health, finances, or legal status, to rigorous review; direct privacy, security, and bias questions to the relevant specialists. Treat prohibited uses as a stop, not as a risk tier that controls can automatically clear.[43][44][45][46]
- Assess: Set evaluation criteria and acceptable thresholds before testing. Review data provenance and quality, relevant performance, fairness, robustness and security, privacy and safety, explainability where needed, and human oversight and recourse. For high-risk uses, bring in relevant legal, privacy, security, ethics, and domain reviewers; use independent validation where warranted and test the integrated workflow.[47][48][49][50]
- Decide and deploy: Record the risk rationale, intended and prohibited uses, data lineage, test results, limitations, mitigations, monitoring plan, owner, reviewers, decision, exceptions, and approved model or system version. Unresolved material risks mean reject, defer, or mitigate and retest. Define rollback conditions, and require re-review when material aspects such as use, users, data access, provider, model version, or operating context change.[51][52][53][54][55]
- Monitor and retire: Track approval measures plus drift, fairness, safety, misuse, unexpected behavior, and use outside scope. Set tier-based monitoring and alert thresholds, assign responders, and schedule reviews. When retiring a system, document the reason and date, manage dependent transitions, and retain the governance evidence trail.[56][57][58]
4. Make escalation routes actionable
The charter should say who can act when a review or monitoring process finds a problem. Provide staff and monitoring systems with a reporting route; define incident severity and urgency, including near misses and recurring or cumulative harms. The system’s operational owner should promptly contain risk, for example by restricting use, invoking human review, or rolling back where warranted, while preserving evidence and notifying relevant governance, security, privacy, legal, and business leads.[59][60][61]
- Escalate to senior leadership or the board when the matter exceeds the committee’s authority or requires an executive or board decision; specify that route and the committee’s reporting line in the charter.[62][63]
- Escalate to the appropriate specialist leads when an incident or assessment involves security, privacy, legal, compliance, or business impacts; identify response roles, communication paths, and evidence handling in advance.[64][65]
- After containment, investigate and close the loop: document root cause, remediation, communications, and follow-up; feed the findings back into risk tiers, controls, and approval criteria. Define whether executive, board, or regulator notification is required under the organization’s circumstances. The research does not establish a universal incident threshold or response deadline, so set these in advance for the organization and applicable obligations.[66][67]
For recurring governance, set a regular meeting schedule, allow urgent meetings, and use working groups or liaisons for specialized or day-to-day reviews. The charter should also specify how often the committee reports and how its records are maintained.[68][69][70]
5. Adapt the framework to the industry
Use one cross-industry backbone, then tailor the review questions and evidence to the harms and obligations of the sector. NIST’s AI Risk Management Framework Playbook organizes suggested actions under Govern, Map, Measure, and Manage; it is voluntary guidance, and organizations can use the portions relevant to their industry and use case rather than treating it as a mandatory checklist.[71][72]
| Setting | Useful starting point | What to emphasize |
|---|---|---|
| Healthcare | CHAI, ABCDS, HEAAL, and the proposed HAIRA maturity model are described in a healthcare governance review.[73][74][75][76] | Patient welfare, health equity, privacy, transparency, accountability, reliability, and ongoing monitoring; the review also describes readiness levels to help organizations set goals suited to their resources.[77][78][79] |
| Finance | Sector guidance recommends applying SR 11-7-style model-risk discipline to LLMs and agents.[80] | Inventory, documentation, monitoring, vendor AI controls, and fair-lending decision lineage for credit-related AI.[81][82] |
| Government | The NIST Playbook is a voluntary, adaptable starting point; a government-sector resource describes lifecycle examples, mitigation strategies, and documentation templates.[83][84] | Use the common lifecycle and documentation guidance, then set review criteria for the agency’s context. The supplied material does not identify a distinct government-only committee framework.[85] |
| Employment | A customizable AI ethics policy template is a starting point, not proof of legal compliance.[86][87] | High-risk review for employment decisions, human oversight, stakeholder engagement, and committee review.[88] |
6. Reusable governance records
Keep the following records together in the AI inventory or registry. These compact templates reflect the recommended intake, decision, monitoring, and incident evidence; tailor required fields to your organization’s risks and applicable obligations.[89][90][91][92]
AI USE-CASE INTAKE
System / use case:
Business owner and operational owner:
Purpose, users, and workflow:
Model / provider and version:
Data sources, sensitivity, and lineage:
Decisions made or informed; affected people:
Risk tier and rationale:
Required reviewers and evidence:

REVIEW DECISION
Criteria and thresholds set before testing:
Evaluation results and known limitations:
Mitigations and residual risks:
Decision: approve / reject / defer / mitigate and retest
Authorized decision-maker; reviewers; date:
Approved version, scope, and prohibited uses:
Monitoring plan, thresholds, and rollback conditions:
Exceptions and follow-up actions:

INCIDENT RECORD
Date, system, reporter, and severity:
Impact, affected people, and evidence preserved:
Containment action and operational owner:
Leads notified; executive / board / regulator notification considered:
Root cause, remediation, and communications:
Reassessment, control changes, and closure owner:
Key takeaway
A workable committee has a written mandate, a mix of technical and affected-stakeholder perspectives, and authority matched to its responsibilities. Connect that authority to a risk-based lifecycle: register systems early, document decisions and evidence, require review before deployment, and give owners a clear path to contain, escalate, and learn from changes or incidents.[93][94][95][96]
Let's look at alternatives:
- Modify the query.
- Start a new thread.
- Remove sources (if manually added).
What makes a weekend digital sabbath effective?
What makes a weekend digital sabbath effective?
A 48-hour digital sabbath is a planned two-day pause from chosen digital habits, designed to make room for rest, connection, and activities you value. It can mean switching off all screens or keeping essential uses, such as calls or maps, while stepping away from feeds and email; the key is to set an intentional boundary rather than treat it as a willpower test.[1][2]
Must-haves for success
- A clear, realistic boundary: Decide in advance which devices or activities are off-limits and what practical exceptions are allowed.[3][4]
- A safety and communication plan: Tell people when you will be offline and agree on an emergency contact route or exception.[5]
- Fewer easy triggers: Silence or log out of tempting apps and place your phone out of reach.[6]
- Offline plans you actually want to do: Prepare options such as a walk, a shared meal, reading, a hobby, or a board game, so screen-free time has something appealing to replace it.[7][8]
Prepare and return deliberately
- Before: Handle urgent work where possible, set an out-of-office message, and arrange offline logistics such as maps, addresses, and travel details.[9][10]
- At the start: Expect some restlessness or automatic phone-checking; have an offline activity ready rather than taking the urge as a sign you have failed.[11]
- At the end: Before reconnecting, reflect briefly on what you reached for, how you used the time, and which boundary you want to keep. Resume devices at a planned time instead of immediately returning to habitual checking.[12][13]
- Afterward: Carry one small, specific practice into everyday life, such as a phone-free meal or screen-free evening; a single weekend is unlikely by itself to change longer-term habits.[14][15]
Let's look at alternatives:
- Modify the query.
- Start a new thread.
- Remove sources (if manually added).
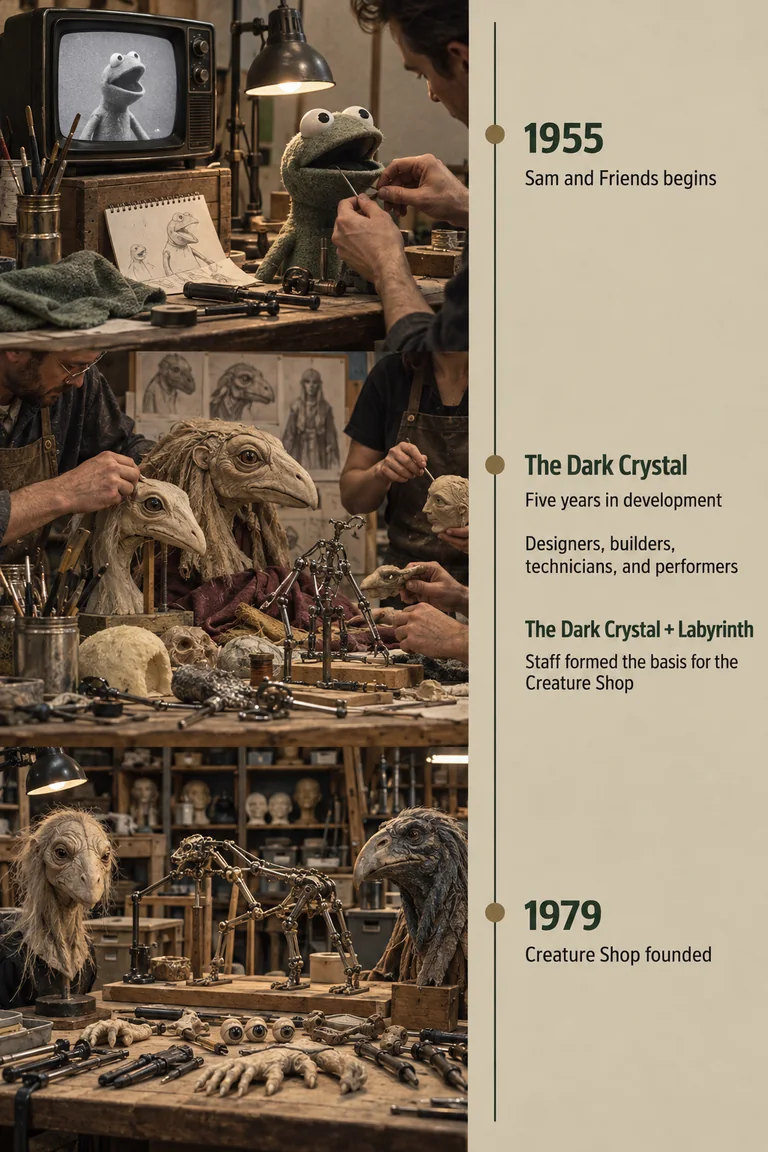
A documented path from television puppetry to the Creature Shop
Let's look at alternatives:
- Modify the query.
- Start a new thread.
- Remove sources (if manually added).