Turn NIST AI RMF into an operating rhythm, not a binder
What if your AI governance model was not a policy shelf, but a closed loop? NIST frames AI RMF as an operating model: Govern, Map, Measure, and Manage should run as an ongoing rhythm tied to the use case and risk profile.[1][2]
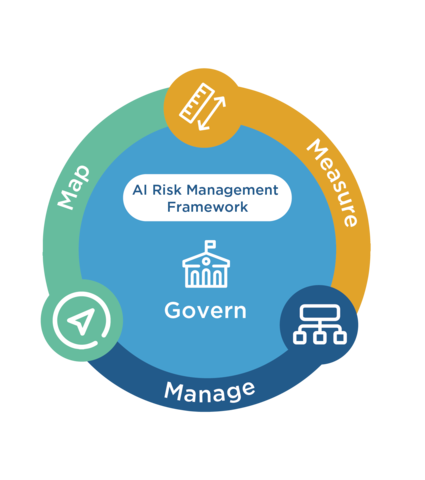
Start with Govern. NIST points to leadership accountability, clear roles and escalation paths, inventories, documentation, training, incident response, and oversight so AI risk management is transparent and actually implemented.[3][4]
Then Map before you build. Define intended purpose, context of use, stakeholders, task scope, risk tolerance, and possible benefits, costs, and harms. That is what lets you prioritize the highest-risk use cases first.[5][6][7]
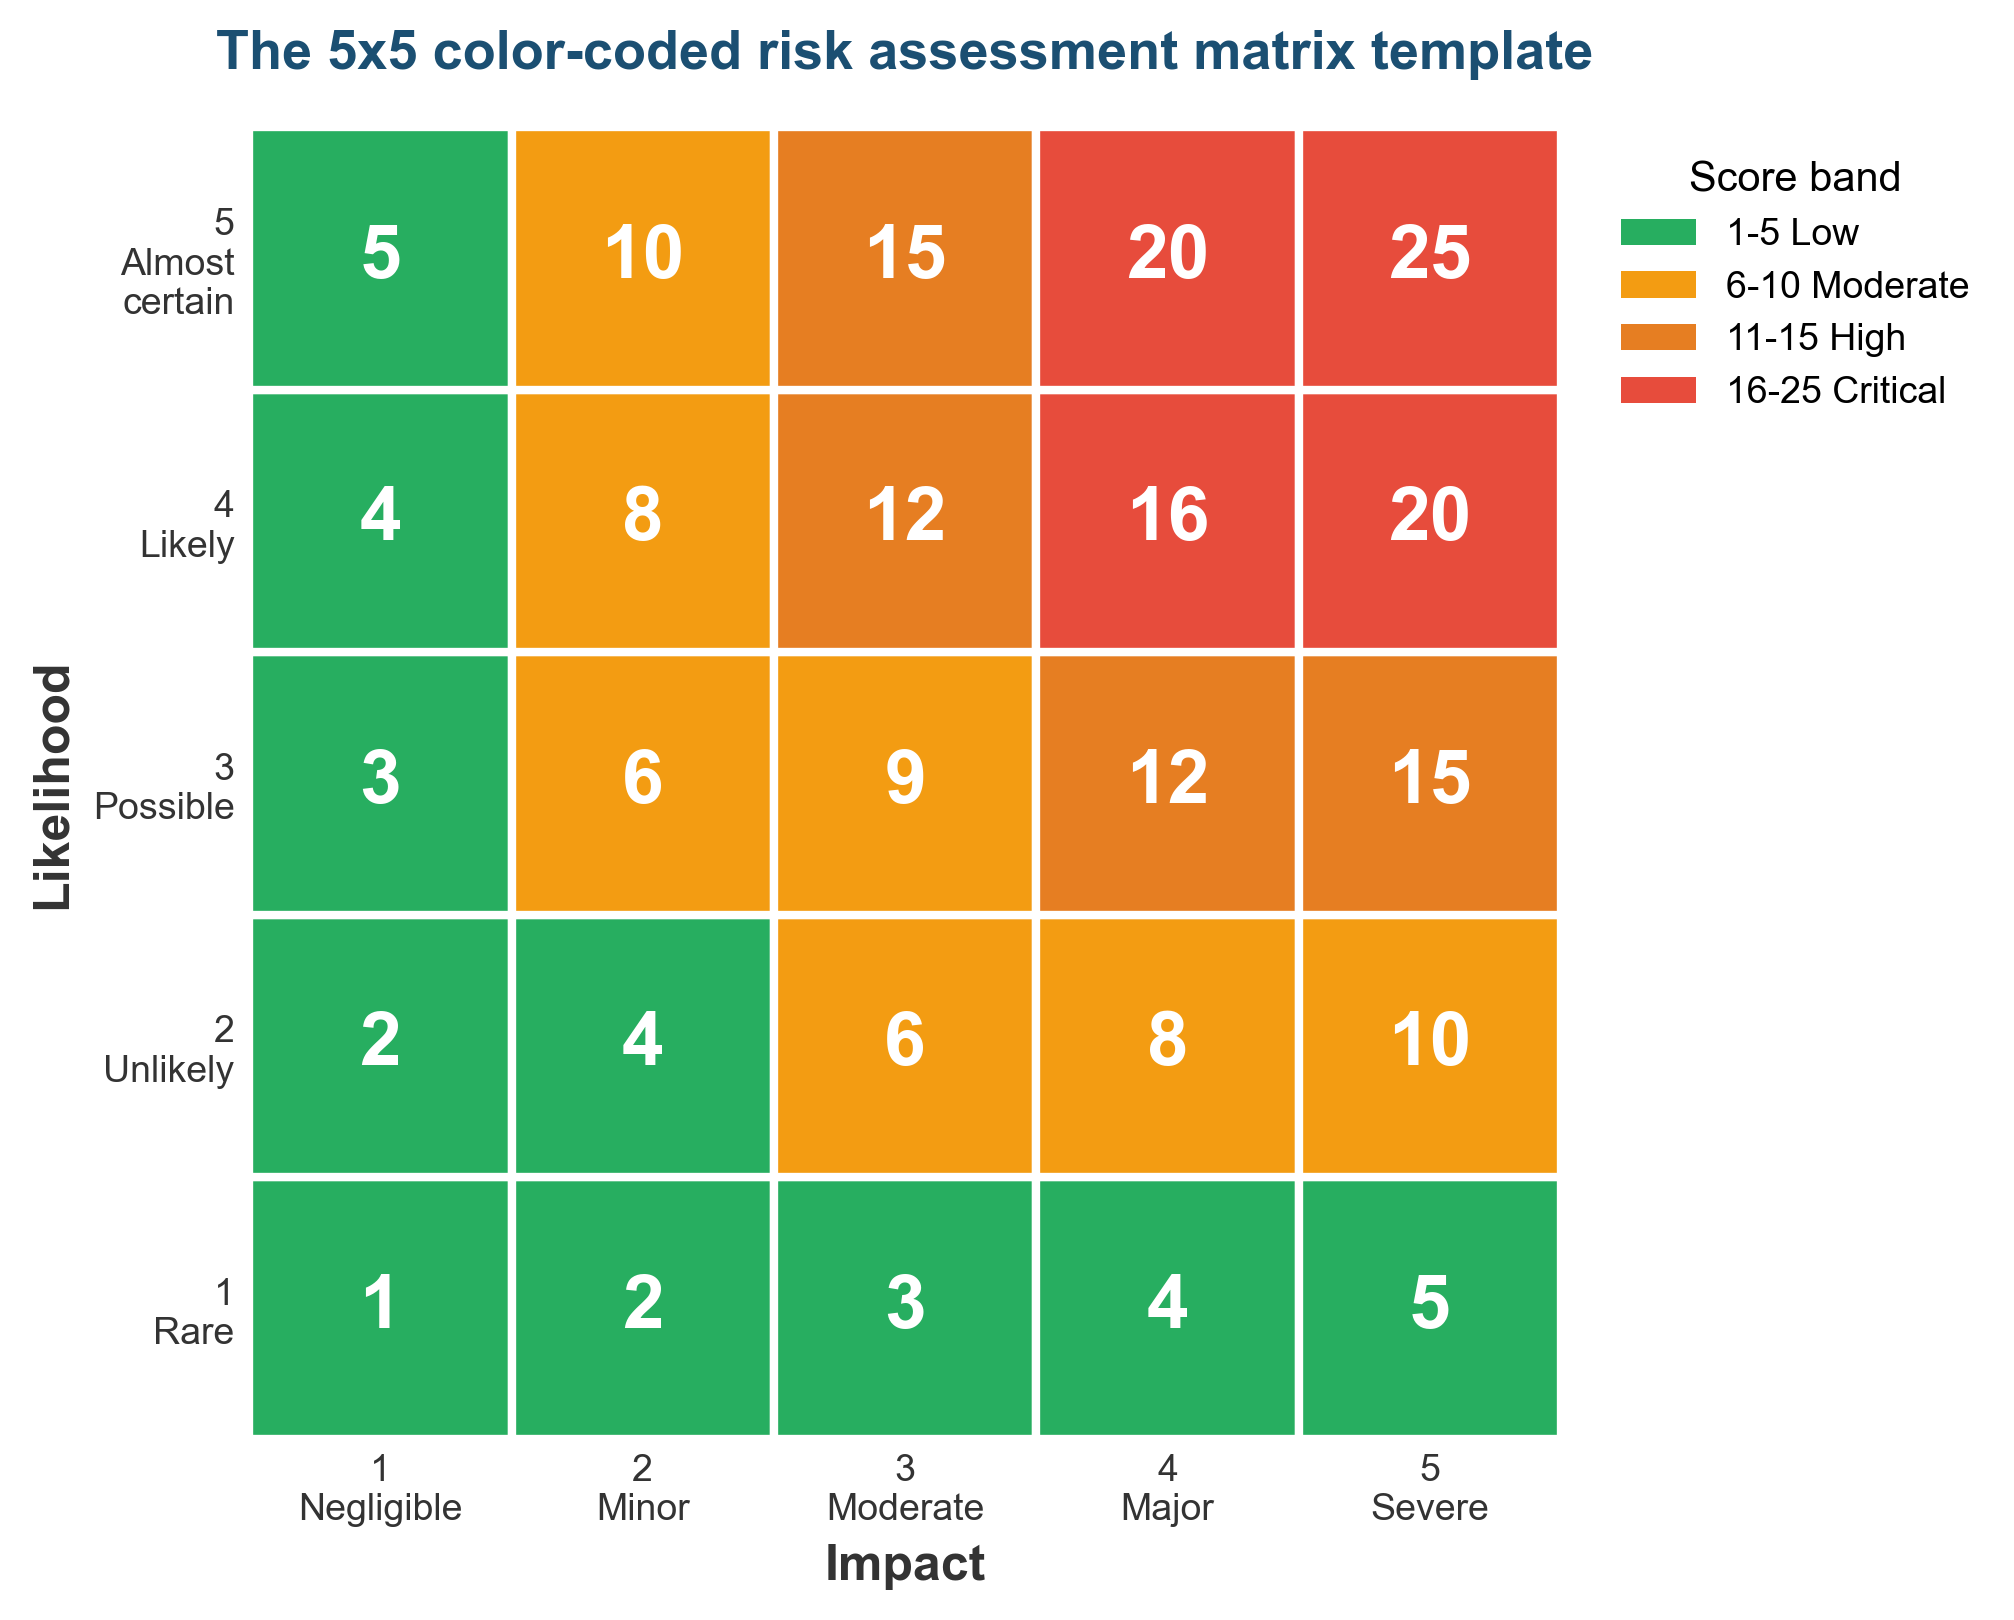
Measure and Manage are the control loop. NIST calls for TEVV methods and metrics for the most significant risks first, plus responses that can include mitigate, transfer, accept, bypass, or decommission, with monitoring and change management after deployment.[8][9][10]

Examinons les alternatives :
- Modifier la requête.
- Démarrer une nouvelle conversation.
- Supprimer des sources (si elles ont été ajoutées manuellement).