Entrada de Pandipedia
LAUNDRY BEAR’s Zimbra chain, from phish to exfil
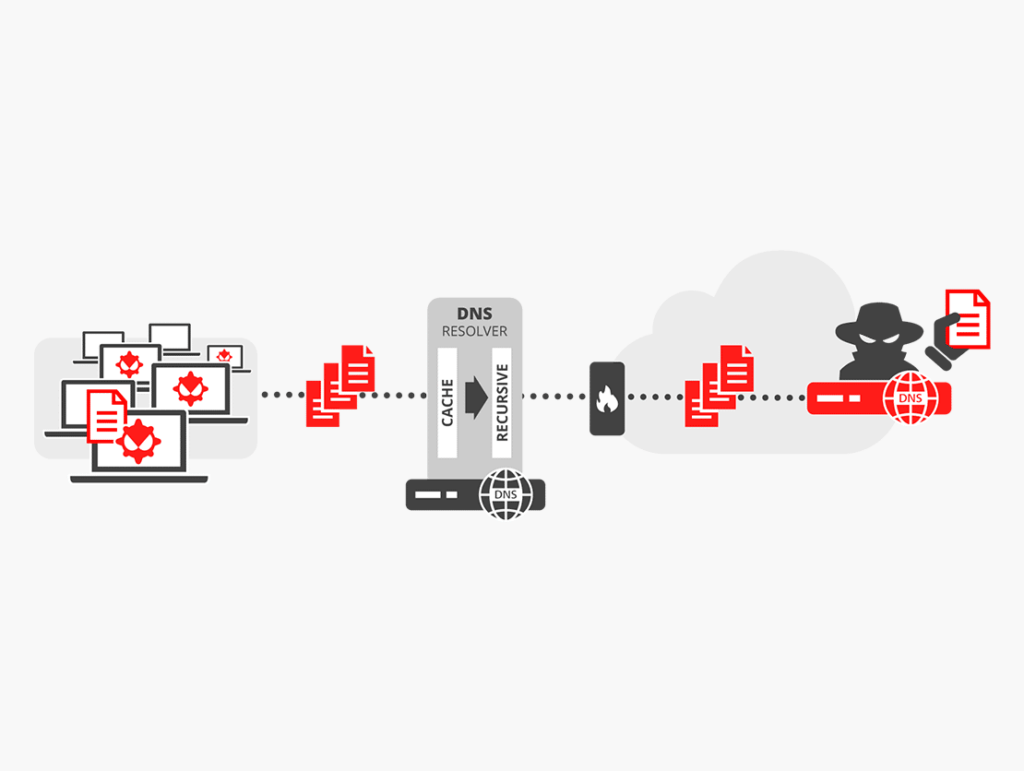
CISA says LAUNDRY BEAR used CVE-2025-66376 in a Zimbra phishing email: viewing it could run JavaScript and start mailbox theft. Hidden in an SVG, the payload passed through Base64/XOR layers and 12 stages. The script sought saved passwords and 2FA scratch codes, enabled IMAP, and created a “ZimbraWeb” Application Passcode. It collected 90 days of mail and sent data over DNS and HTTPS. CISA advised patching to ZCS 10.1.13 or 10.0.18 and avoiding Classic webmail until patched.
Ho sentim, Pandi no ha pogut trobar una resposta.
Veiem alternatives:
- Modifica la consulta.
- Inicia un nou fil.
- Elimina les fonts (si s'han afegit manualment).